Krishna Radhakeesoon
Partner - IT Governance & Consulting
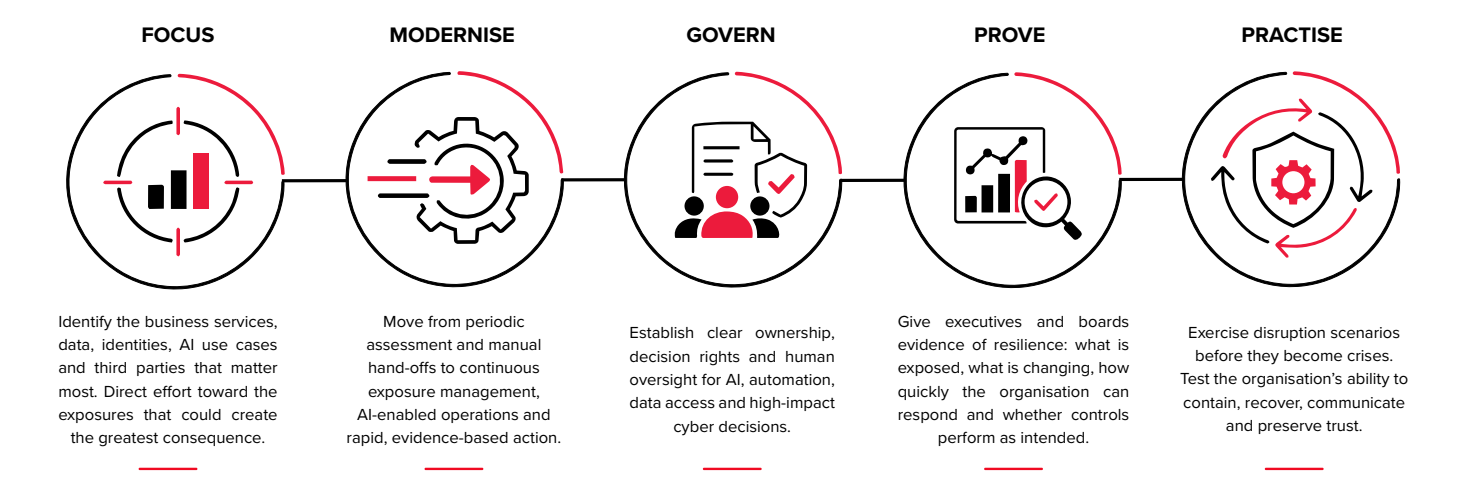
Cybersecurity has become a speed problem, not a skill problem. The future belongs to organisations who anticipate, adapt and act continuously, while keeping people firmly in control of consequential decisions.
The purpose of cybersecurity hasn’t changed. We still protect systems, data, people and critical operations. What is changing is how cyber teams engage, how quickly they need to make decisions and how deeply integrated security must be with business transformation.
The days of bringing cyber teams in at the end of a technology initiative to test what has already been built are far behind us. We have to bring cyber in at the beginning, helping the organisation move safely, confidently and quickly.
That shift matters because technology is becoming easier to deploy but much more difficult to govern. Cloud platforms, connected ecosystems and AI allow business teams to create new capabilities at amazing speeds. They also expand the number of identities, service accounts, interfaces, suppliers and autonomous agents that can touch sensitive data or make decisions. When we think about the perimeter we are trying to protect, it has not disappeared. It continues to multiply exponentially.
AI is not just another technology risk. It changes the pace of cyber. Tasks that once demanded scarce expertise, manual research and extended preparation can increasingly be assisted or automated. Discovery, targeting, social engineering and exploitation all move faster with the capabilities this new technology affords us. At the same time, defenders can use AI to enrich alerts, prioritise exposure, automate high-confidence actions and reduce the burden on analysts. The next era won’t be human versus human. It will be human and machine versus human and machine.
This is why the old human-first operating model has become a risk. Alerts, tickets, hand-offs and scheduled patch cycles remain useful, but they were designed for a slower environment. The future model is continuous: always learning, always assessing and ready to act. It pairs machine-speed detection and containment with human judgment, business context and accountability. Automation needs to move decisively when confidence is high, and the risk of delay is greater than the risk of action. Human oversight remains essential where safety, critical services or material business consequences are involved.
Traditional programmes have often measured activity: numbers of vulnerabilities, patching cycles completed, alerts reviewed or policies published. Those measures can create comfort without proving resilience. Leaders increasingly need to understand actual exposure. Which vulnerabilities are exploitable? Which identities have unnecessary access? Which third parties create concentration risk? How quickly can the organisation detect, contain, recover and explain?
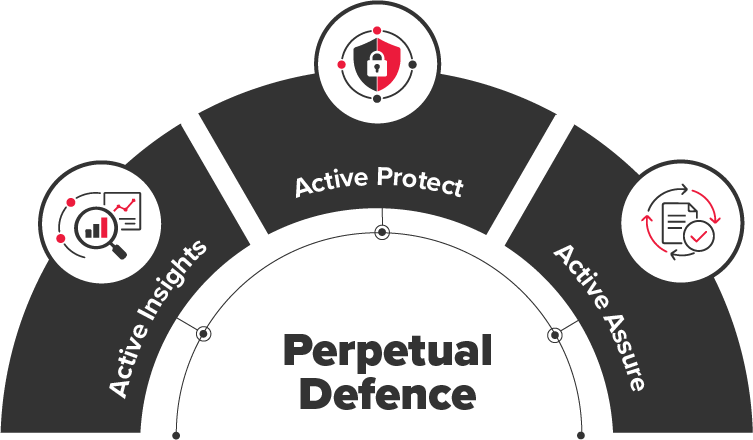
The future of cybersecurity is framed as an always-on capability that connects strategy, operations and assurance and in BDOs view Active Insights, Active Protect, Active Assure. Static threat models transition to dynamic learning. Periodic assessments evolve into continuous exposure management. Vulnerability lists become vulnerability operations, with immediate analysis and action. Reactive incident response becomes more predictive and pre-emptive response through ongoing testing and simulations. Point-in-time compliance becomes evidence controls are operating, adapting and producing the intended business outcome.
Our three-part, end-to-end Perpetual Defence security framework provides pre-emptive threat management that adapts to evolving cybersecurity risks.
Comprehensive preparation services that ensures your organization’s digital transformation journey is secured and resilient against evolving cyber threats. With a focus on driving optimization and cost efficiency, we assess your current state and assist in planning for improvements, centered around your people, processes, and technology.
Active Protect ensures visibility of your key digital assets through 24x7x365 monitoring, allowing for rapid detection and response of cyber threats in near real-time. We cover all your points of presence to reduce the likelihood of adversaries establishing a foothold in your organization.
BDO’s Active Assure solution provides confidence through our Operational and Offensive security testing services. These services use technical testing methods to assess your security posture and quickly identify areas for improvement and remediation. The goal is to provide insight into the effectiveness of your cyber hygiene, controls, and development practices.
The future of cybersecurity won’t be secured through incremental improvement alone. Leaders need to act now, with a focused agenda that connects cyber investment to business priorities, accelerates decision-making and builds resilience into the way the organisation operates.