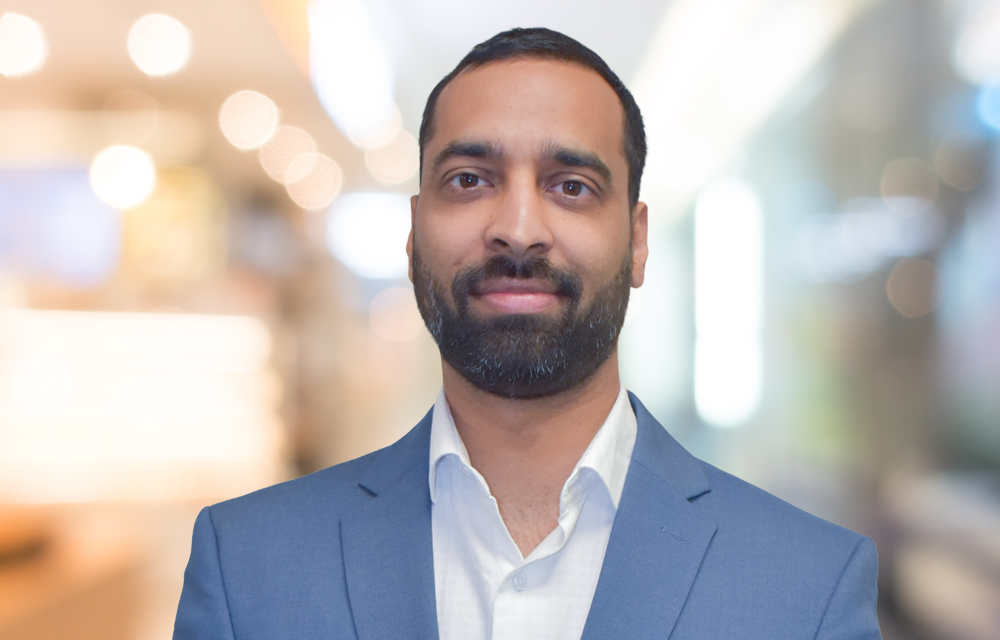
Kavish Boodhoo
Information Security & Governance Lead
Contact
Executive summary
Kavish has over 12 years of professional experience, including more than 9 years specialising in information security, advising organisations across the public and private sectors in Mauritius, Africa, Europe and the United Kingdom. His experience spans financial services, insurance, technology, aviation, energy and other commercial sectors.
His expertise combines cybersecurity, IT governance, technology risk and regulatory compliance, with experience delivering both technical security assessments and governance-focused engagements. Kavish has particular experience supporting organisations with DORA and NIS2 requirements, third-party risk management, ISO/IEC 27001, business continuity and SWIFT CSP assessments.
CERTIFICATIONS
His expertise combines cybersecurity, IT governance, technology risk and regulatory compliance, with experience delivering both technical security assessments and governance-focused engagements. Kavish has particular experience supporting organisations with DORA and NIS2 requirements, third-party risk management, ISO/IEC 27001, business continuity and SWIFT CSP assessments.
He has led DORA and NIS2 compliance initiatives for large European organisations and has conducted multi-jurisdictional third-party and vendor risk assessments for financial institutions operating across Africa.
AREAS OF EXPERTISE
AREAS OF EXPERTISE
- Cybersecurity and technology risk assessments
- Vulnerability assessment and security testing
- Third-Party Risk Management and vendor risk assessments
- DORA and NIS2 compliance and readiness
- ISO/IEC 27001 information security audits
- ISO 22301 business continuity and operational resilience
- SWIFT Customer Security Programme assessments
- Threat analysis and security control assessments
- IT governance and regulatory compliance
- Data analytics and migration reviews
CERTIFICATIONS
- CompTIA SecurityX (Formerly Certified Advanced Security Practitioner)
- CompTIA CySA+ (Cybersecurity Analyst)
- ISO 27001 Senior Lead Auditor
- ISO 22301 Lead Auditor
- ISO 31000 Senior Lead Risk Manager
- Certified DORA Senior Lead Manager
- Certified Senior Lead Cybersecurity Manager
- Certified ISO 27002 Lead Manager
- Diploma in Information Technology